Ansible一键安装Harbor服务
环境说明
本次实验使用在ESXI6.7环境下最小化安装(没有图形化界面)的AlmaLinux9.4全新安装系统。采用docker-compose的方式安装Harbor服务,需要先安装docker、docker-compose两个服务,将以二进制的方式安装docker和docker-compose,以适配各种安装环境。
- docker版本:20.10.24,建议使用20.10以上的版本,低版本的会出现安装异常;
- Docker-compose版本:2.24.7
- Harbor版本:2.10.3
一、编写ansible role
1.0 安装ansible
使用过下面的命令安装epel仓库和ansible
$ dnf update -y
$ dnf install -y epel-release
$ dnf install -y ansible
执行的结果
[root@Harbor ~]# dnf install -y epel-release
上次元数据过期检查:0:07:01 前,执行于 2024年08月22日 星期四 10时33分41秒。
依赖关系解决。
================================================================================
 软件包                架构            版本               仓库             大小
================================================================================
安装:
 epel-release          noarch          9-5.el9            extras           18 k

事务概要
================================================================================
安装  1 软件包

总下载:18 k
安装大小:25 k
下载软件包:
epel-release-9-5.el9.noarch.rpm                 121 kB/s |  18 kB     00:00
--------------------------------------------------------------------------------
总计                                             19 kB/s |  18 kB     00:00
运行事务检查
事务检查成功。
运行事务测试
事务测试成功。
运行事务
  准备中  :                                                                 1/1
  安装    : epel-release-9-5.el9.noarch                                     1/1
  运行脚本: epel-release-9-5.el9.noarch                                     1/1
Many EPEL packages require the CodeReady Builder (CRB) repository.
It is recommended that you run /usr/bin/crb enable to enable the CRB repository.

  验证    : epel-release-9-5.el9.noarch                                     1/1

已安装:
  epel-release-9-5.el9.noarch

完毕!
[root@Harbor ~]# dnf install -y ansible
Extra Packages for Enterprise Linux 9 - x86_64  1.3 MB/s |  22 MB     00:17
上次元数据过期检查:0:00:09 前,执行于 2024年08月22日 星期四 10时41分05秒。
依赖关系解决。
================================================================================
 软件包                   架构       版本                   仓库           大小
================================================================================
安装:
 ansible                  noarch     1:7.7.0-1.el9          epel           34 M
安装依赖关系:
 ansible-core             x86_64     1:2.14.14-1.el9        appstream     2.2 M
 git-core                 x86_64     2.43.5-1.el9_4         appstream     4.4 M
 python3-cffi             x86_64     1.14.5-5.el9           baseos        241 k
 python3-cryptography     x86_64     36.0.1-4.el9           baseos        1.1 M
 python3-packaging        noarch     20.9-5.el9             appstream      69 k
 python3-ply              noarch     3.11-14.el9            baseos        103 k
 python3-pycparser        noarch     2.20-6.el9             baseos        124 k
 python3-pyparsing        noarch     2.4.7-9.el9            baseos        149 k
 python3-pyyaml           x86_64     5.4.1-6.el9            baseos        190 k
 python3-resolvelib       noarch     0.5.4-5.el9            appstream      29 k
 python3-setuptools       noarch     53.0.0-12.el9_4.1      baseos        838 k
 sshpass                  x86_64     1.09-4.el9             appstream      27 k

事务概要
================================================================================
安装  13 软件包

总下载:44 M
安装大小:408 M
下载软件包:
(1/13): python3-packaging-20.9-5.el9.noarch.rpm 252 kB/s |  69 kB     00:00
(2/13): python3-resolvelib-0.5.4-5.el9.noarch.r 505 kB/s |  29 kB     00:00
(3/13): sshpass-1.09-4.el9.x86_64.rpm           344 kB/s |  27 kB     00:00
(4/13): ansible-core-2.14.14-1.el9.x86_64.rpm   4.8 MB/s | 2.2 MB     00:00
(5/13): git-core-2.43.5-1.el9_4.x86_64.rpm      7.7 MB/s | 4.4 MB     00:00
(6/13): python3-cffi-1.14.5-5.el9.x86_64.rpm    1.2 MB/s | 241 kB     00:00
(7/13): python3-ply-3.11-14.el9.noarch.rpm      1.5 MB/s | 103 kB     00:00
(8/13): python3-cryptography-36.0.1-4.el9.x86_6 5.8 MB/s | 1.1 MB     00:00
(9/13): python3-pycparser-2.20-6.el9.noarch.rpm 1.4 MB/s | 124 kB     00:00
(10/13): python3-pyyaml-5.4.1-6.el9.x86_64.rpm  2.6 MB/s | 190 kB     00:00
(11/13): python3-pyparsing-2.4.7-9.el9.noarch.r 1.6 MB/s | 149 kB     00:00
(12/13): python3-setuptools-53.0.0-12.el9_4.1.n 3.5 MB/s | 838 kB     00:00
(13/13): ansible-7.7.0-1.el9.noarch.rpm         5.8 MB/s |  34 MB     00:05
--------------------------------------------------------------------------------
总计                                            5.2 MB/s |  44 MB     00:08
Extra Packages for Enterprise Linux 9 - x86_64  1.6 MB/s | 1.6 kB     00:00
导入 GPG 公钥 0x3228467C:
 Userid: "Fedora (epel9) <epel@fedoraproject.org>"
 指纹: FF8A D134 4597 106E CE81 3B91 8A38 72BF 3228 467C
 来自: /etc/pki/rpm-gpg/RPM-GPG-KEY-EPEL-9
导入公钥成功
运行事务检查
事务检查成功。
运行事务测试
事务测试成功。
运行事务
  准备中  :                                                                 1/1
  安装    : python3-setuptools-53.0.0-12.el9_4.1.noarch                    1/13
  安装    : python3-pyyaml-5.4.1-6.el9.x86_64                              2/13
  安装    : python3-pyparsing-2.4.7-9.el9.noarch                           3/13
  安装    : python3-packaging-20.9-5.el9.noarch                            4/13
  安装    : python3-ply-3.11-14.el9.noarch                                 5/13
  安装    : python3-pycparser-2.20-6.el9.noarch                            6/13
  安装    : python3-cffi-1.14.5-5.el9.x86_64                               7/13
  安装    : python3-cryptography-36.0.1-4.el9.x86_64                       8/13
  安装    : sshpass-1.09-4.el9.x86_64                                      9/13
  安装    : python3-resolvelib-0.5.4-5.el9.noarch                         10/13
  安装    : git-core-2.43.5-1.el9_4.x86_64                                11/13
  安装    : ansible-core-1:2.14.14-1.el9.x86_64                           12/13
  安装    : ansible-1:7.7.0-1.el9.noarch                                  13/13
  运行脚本: ansible-1:7.7.0-1.el9.noarch                                  13/13
  验证    : ansible-core-1:2.14.14-1.el9.x86_64                            1/13
  验证    : git-core-2.43.5-1.el9_4.x86_64                                 2/13
  验证    : python3-packaging-20.9-5.el9.noarch                            3/13
  验证    : python3-resolvelib-0.5.4-5.el9.noarch                          4/13
  验证    : sshpass-1.09-4.el9.x86_64                                      5/13
  验证    : python3-cffi-1.14.5-5.el9.x86_64                               6/13
  验证    : python3-cryptography-36.0.1-4.el9.x86_64                       7/13
  验证    : python3-ply-3.11-14.el9.noarch                                 8/13
  验证    : python3-pycparser-2.20-6.el9.noarch                            9/13
  验证    : python3-pyparsing-2.4.7-9.el9.noarch                          10/13
  验证    : python3-pyyaml-5.4.1-6.el9.x86_64                             11/13
  验证    : python3-setuptools-53.0.0-12.el9_4.1.noarch                   12/13
  验证    : ansible-1:7.7.0-1.el9.noarch                                  13/13

已安装:
  ansible-1:7.7.0-1.el9.noarch
  ansible-core-1:2.14.14-1.el9.x86_64
  git-core-2.43.5-1.el9_4.x86_64
  python3-cffi-1.14.5-5.el9.x86_64
  python3-cryptography-36.0.1-4.el9.x86_64
  python3-packaging-20.9-5.el9.noarch
  python3-ply-3.11-14.el9.noarch
  python3-pycparser-2.20-6.el9.noarch
  python3-pyparsing-2.4.7-9.el9.noarch
  python3-pyyaml-5.4.1-6.el9.x86_64
  python3-resolvelib-0.5.4-5.el9.noarch
  python3-setuptools-53.0.0-12.el9_4.1.noarch
  sshpass-1.09-4.el9.x86_64

完毕!
使用ansible --version查看ansible的版本信息,确认ansible已经正确安装
[root@Harbor ~]# ansible --version
ansible [core 2.14.14]
  config file = /etc/ansible/ansible.cfg
  configured module search path = ['/root/.ansible/plugins/modules', '/usr/share/ansible/plugins/modules']
  ansible python module location = /usr/lib/python3.9/site-packages/ansible
  ansible collection location = /root/.ansible/collections:/usr/share/ansible/collections
  executable location = /usr/bin/ansible
  python version = 3.9.18 (main, Jul  3 2024, 00:00:00) [GCC 11.4.1 20231218 (Red Hat 11.4.1-3)] (/usr/bin/python3)
  jinja version = 3.1.2
  libyaml = True
1.1 初始化ansible role
使用ansible-galaxy init命令初始化一个安装harbor的ansible role。
[root@Harbor ~]# ansible-galaxy init /etc/ansible/roles/harbor-install
- Role /etc/ansible/roles/harbor-install was created successfully
1.2 设置环境变量
通过环境变量的方式自定义安装环境,使用时候修改对应环境变量的值即可。
$ cat roles/harbor-install/vars/main.yml
---
# vars file for harbor-install
DOCKER_VERSION: "20.10.24"  #docker服务版本
HARBOR_VERSION: 2.10.3     #harbor服务版本
INSTALL_PATH: /app         #安装目录
HTTP_PORT: 8888            #harbor服务端口(http)
HTTPS_PORT:                #harbor服务端口(https)
DATA_PATH: /app/data       #harbor数据目录,规划好大小
1.3 下载文件
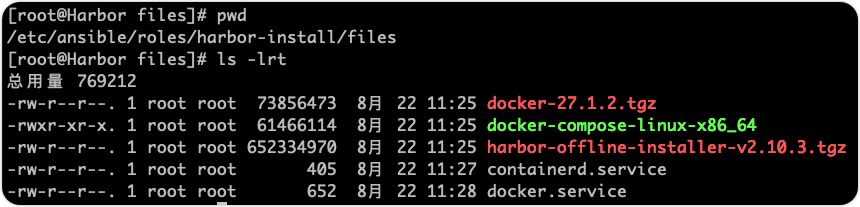
因为考虑到后续如果是在不能连接互联网的企业内网环境中也可以使用,提前将对应版本的安装包下载好放到roles/harbor-install/files/目录下。
[root@Harbor ~]# cd /etc/ansible/roles/harbor-install/files
[root@Harbor ~]# wget -c https://download.docker.com/linux/static/stable/x86_64/docker-27.1.2.tgz
[root@Harbor ~]# wget -c https://github.com/docker/compose/releases/download/v2.24.7/docker-compose-linux-x86_64
[root@Harbor ~]# wget -c https://github.com/goharbor/harbor/releases/download/v2.10.3/harbor-offline-installer-v2.10.3.tgz
1.4 创建服务启动文件
安装harbor时依赖docker和containerd两个服务,将服务启动文件写好放到role/harbor-install/files/目录下。
- 创建containerd服务启动文件
$ cat role/harbor-install/files/containerd.service
[Unit]
Description=containerd container runtime
Documentation=https://containerd.io
After=network.target local-fs.target

[Service]
ExecStartPre=-/sbin/modprobe overlay
ExecStart=/usr/bin/containerd

Type=notify
Delegate=yes
KillMode=process
Restart=always
RestartSec=5
LimitNPROC=infinity
LimitCORE=infinity
LimitNOFILE=1048576
TasksMax=infinity
OOMScoreAdjust=-999

[Install]
WantedBy=multi-user.target
- 创建docker启动文件
$ cat role/harbor-install/files/docker.service
[Unit]
Description=Docker Application Container Engine
Documentation=https://docs.docker.com
After=network-online.target docker.socket firewalld.service containerd.service time-set.target
Wants=network-online.target containerd.service
Requires=docker.socket

[Service]
Type=notify
ExecStart=/usr/bin/dockerd -H fd:// --containerd=/run/containerd/containerd.sock
ExecReload=/bin/kill -s HUP $MAINPID
TimeoutStartSec=0
RestartSec=2
Restart=always
StartLimitBurst=3
StartLimitInterval=60s
LimitNOFILE=infinity
LimitNPROC=infinity
LimitCORE=infinity
TasksMax=infinity
Delegate=yes
KillMode=process
OOMScoreAdjust=-500

[Install]
WantedBy=multi-user.target
1.5 创建Harbor配置文件模块
使用jinjia2模板文件来根据环境变量自动生成Harbor的配置文件。
$ cat /etc/ansible/roles/harbor-install/templates/harbor.yml.j2
# Configuration file of Harbor

# The IP address or hostname to access admin UI and registry service.
# DO NOT use localhost or 127.0.0.1, because Harbor needs to be accessed by external clients.
hostname: {{ ansible_host }}

# http related config
http:
  # port for http, default is 80. If https enabled, this port will redirect to https port
  port: {{ HTTP_PORT }}

# https related config
#https:
  # https port for harbor, default is 443
  #port: 443
  # The path of cert and key files for nginx
  #certificate: /your/certificate/path
  #private_key: /your/private/key/path
  # enable strong ssl ciphers (default: false)
  # strong_ssl_ciphers: false

# # Uncomment following will enable tls communication between all harbor components
# internal_tls:
#   # set enabled to true means internal tls is enabled
#   enabled: true
#   # put your cert and key files on dir
#   dir: /etc/harbor/tls/internal


# Uncomment external_url if you want to enable external proxy
# And when it enabled the hostname will no longer used
# external_url: https://reg.mydomain.com:8433
external_url: http://{{ ansible_host }}:{{ HTTP_PORT }}

# The initial password of Harbor admin
# It only works in first time to install harbor
# Remember Change the admin password from UI after launching Harbor.
harbor_admin_password: Harbor12345

# Harbor DB configuration
database:
  # The password for the root user of Harbor DB. Change this before any production use.
  password: root123
  # The maximum number of connections in the idle connection pool. If it <=0, no idle connections are retained.
  max_idle_conns: 100
  # The maximum number of open connections to the database. If it <= 0, then there is no limit on the number of open connections.
  # Note: the default number of connections is 1024 for postgres of harbor.
  max_open_conns: 900
  # The maximum amount of time a connection may be reused. Expired connections may be closed lazily before reuse. If it <= 0, connections are not closed due to a connection's age.
  # The value is a duration string. A duration string is a possibly signed sequence of decimal numbers, each with optional fraction and a unit suffix, such as "300ms", "-1.5h" or "2h45m". Valid time units are "ns", "us" (or "µs"), "ms", "s", "m", "h".
  conn_max_lifetime: 5m
  # The maximum amount of time a connection may be idle. Expired connections may be closed lazily before reuse. If it <= 0, connections are not closed due to a connection's idle time.
  # The value is a duration string. A duration string is a possibly signed sequence of decimal numbers, each with optional fraction and a unit suffix, such as "300ms", "-1.5h" or "2h45m". Valid time units are "ns", "us" (or "µs"), "ms", "s", "m", "h".
  conn_max_idle_time: 0

# The default data volume
data_volume: /data

# Harbor Storage settings by default is using /data dir on local filesystem
# Uncomment storage_service setting If you want to using external storage
# storage_service:
#   # ca_bundle is the path to the custom root ca certificate, which will be injected into the truststore
#   # of registry's containers.  This is usually needed when the user hosts a internal storage with self signed certificate.
#   ca_bundle:

#   # storage backend, default is filesystem, options include filesystem, azure, gcs, s3, swift and oss
#   # for more info about this configuration please refer https://docs.docker.com/registry/configuration/
#   filesystem:
#     maxthreads: 100
#   # set disable to true when you want to disable registry redirect
#   redirect:
#     disable: false

# Trivy configuration
#
# Trivy DB contains vulnerability information from NVD, Red Hat, and many other upstream vulnerability databases.
# It is downloaded by Trivy from the GitHub release page https://github.com/aquasecurity/trivy-db/releases and cached
# in the local file system. In addition, the database contains the update timestamp so Trivy can detect whether it
# should download a newer version from the Internet or use the cached one. Currently, the database is updated every
# 12 hours and published as a new release to GitHub.
trivy:
  # ignoreUnfixed The flag to display only fixed vulnerabilities
  ignore_unfixed: false
  # skipUpdate The flag to enable or disable Trivy DB downloads from GitHub
  #
  # You might want to enable this flag in test or CI/CD environments to avoid GitHub rate limiting issues.
  # If the flag is enabled you have to download the `trivy-offline.tar.gz` archive manually, extract `trivy.db` and
  # `metadata.json` files and mount them in the `/home/scanner/.cache/trivy/db` path.
  skip_update: false
  #
  # skipJavaDBUpdate If the flag is enabled you have to manually download the `trivy-java.db` file and mount it in the
  # `/home/scanner/.cache/trivy/java-db/trivy-java.db` path
  skip_java_db_update: false
  #
  # The offline_scan option prevents Trivy from sending API requests to identify dependencies.
  # Scanning JAR files and pom.xml may require Internet access for better detection, but this option tries to avoid it.
  # For example, the offline mode will not try to resolve transitive dependencies in pom.xml when the dependency doesn't
  # exist in the local repositories. It means a number of detected vulnerabilities might be fewer in offline mode.
  # It would work if all the dependencies are in local.
  # This option doesn't affect DB download. You need to specify "skip-update" as well as "offline-scan" in an air-gapped environment.
  offline_scan: false
  #
  # Comma-separated list of what security issues to detect. Possible values are `vuln`, `config` and `secret`. Defaults to `vuln`.
  security_check: vuln
  #
  # insecure The flag to skip verifying registry certificate
  insecure: false
  # github_token The GitHub access token to download Trivy DB
  #
  # Anonymous downloads from GitHub are subject to the limit of 60 requests per hour. Normally such rate limit is enough
  # for production operations. If, for any reason, it's not enough, you could increase the rate limit to 5000
  # requests per hour by specifying the GitHub access token. For more details on GitHub rate limiting please consult
  # https://docs.github.com/rest/overview/resources-in-the-rest-api#rate-limiting
  #
  # You can create a GitHub token by following the instructions in
  # https://help.github.com/en/github/authenticating-to-github/creating-a-personal-access-token-for-the-command-line
  #
  # github_token: xxx

jobservice:
  # Maximum number of job workers in job service
  max_job_workers: 10
  # The jobLoggers backend name, only support "STD_OUTPUT", "FILE" and/or "DB"
  job_loggers:
    - STD_OUTPUT
    - FILE
    # - DB
  # The jobLogger sweeper duration (ignored if `jobLogger` is `stdout`)
  logger_sweeper_duration: 1 #days

notification:
  # Maximum retry count for webhook job
  webhook_job_max_retry: 3
  # HTTP client timeout for webhook job
  webhook_job_http_client_timeout: 3 #seconds

# Log configurations
log:
  # options are debug, info, warning, error, fatal
  level: info
  # configs for logs in local storage
  local:
    # Log files are rotated log_rotate_count times before being removed. If count is 0, old versions are removed rather than rotated.
    rotate_count: 50
    # Log files are rotated only if they grow bigger than log_rotate_size bytes. If size is followed by k, the size is assumed to be in kilobytes.
    # If the M is used, the size is in megabytes, and if G is used, the size is in gigabytes. So size 100, size 100k, size 100M and size 100G
    # are all valid.
    rotate_size: 200M
    # The directory on your host that store log
    location: /var/log/harbor

  # Uncomment following lines to enable external syslog endpoint.
  # external_endpoint:
  #   # protocol used to transmit log to external endpoint, options is tcp or udp
  #   protocol: tcp
  #   # The host of external endpoint
  #   host: localhost
  #   # Port of external endpoint
  #   port: 5140

#This attribute is for migrator to detect the version of the .cfg file, DO NOT MODIFY!
_version: 2.10.0

# Uncomment external_database if using external database.
# external_database:
#   harbor:
#     host: harbor_db_host
#     port: harbor_db_port
#     db_name: harbor_db_name
#     username: harbor_db_username
#     password: harbor_db_password
#     ssl_mode: disable
#     max_idle_conns: 2
#     max_open_conns: 0

# Uncomment redis if need to customize redis db
# redis:
#   # db_index 0 is for core, it's unchangeable
#   # registry_db_index: 1
#   # jobservice_db_index: 2
#   # trivy_db_index: 5
#   # it's optional, the db for harbor business misc, by default is 0, uncomment it if you want to change it.
#   # harbor_db_index: 6
#   # it's optional, the db for harbor cache layer, by default is 0, uncomment it if you want to change it.
#   # cache_db_index: 7

# Uncomment redis if need to customize redis db
# redis:
#   # db_index 0 is for core, it's unchangeable
#   # registry_db_index: 1
#   # jobservice_db_index: 2
#   # trivy_db_index: 5
#   # it's optional, the db for harbor business misc, by default is 0, uncomment it if you want to change it.
#   # harbor_db_index: 6
#   # it's optional, the db for harbor cache layer, by default is 0, uncomment it if you want to change it.
#   # cache_layer_db_index: 7

# Uncomment external_redis if using external Redis server
# external_redis:
#   # support redis, redis+sentinel
#   # host for redis: <host_redis>:<port_redis>
#   # host for redis+sentinel:
#   #  <host_sentinel1>:<port_sentinel1>,<host_sentinel2>:<port_sentinel2>,<host_sentinel3>:<port_sentinel3>
#   host: redis:6379
#   password:
#   # Redis AUTH command was extended in Redis 6, it is possible to use it in the two-arguments AUTH <username> <password> form.
#   # there's a known issue when using external redis username ref:https://github.com/goharbor/harbor/issues/18892
#   # if you care about the image pull/push performance, please refer to this https://github.com/goharbor/harbor/wiki/Harbor-FAQs#external-redis-username-password-usage
#   # username:
#   # sentinel_master_set must be set to support redis+sentinel
#   #sentinel_master_set:
#   # db_index 0 is for core, it's unchangeable
#   registry_db_index: 1
#   jobservice_db_index: 2
#   trivy_db_index: 5
#   idle_timeout_seconds: 30
#   # it's optional, the db for harbor business misc, by default is 0, uncomment it if you want to change it.
#   # harbor_db_index: 6
#   # it's optional, the db for harbor cache layer, by default is 0, uncomment it if you want to change it.
#   # cache_layer_db_index: 7

# Uncomment uaa for trusting the certificate of uaa instance that is hosted via self-signed cert.
# uaa:
#   ca_file: /path/to/ca

# Global proxy
# Config http proxy for components, e.g. http://my.proxy.com:3128
# Components doesn't need to connect to each others via http proxy.
# Remove component from `components` array if want disable proxy
# for it. If you want use proxy for replication, MUST enable proxy
# for core and jobservice, and set `http_proxy` and `https_proxy`.
# Add domain to the `no_proxy` field, when you want disable proxy
# for some special registry.
proxy:
  http_proxy:
  https_proxy:
  no_proxy:
  components:
    - core
    - jobservice
    - trivy

# metric:
#   enabled: false
#   port: 9090
#   path: /metrics

# Trace related config
# only can enable one trace provider(jaeger or otel) at the same time,
# and when using jaeger as provider, can only enable it with agent mode or collector mode.
# if using jaeger collector mode, uncomment endpoint and uncomment username, password if needed
# if using jaeger agetn mode uncomment agent_host and agent_port
# trace:
#   enabled: true
#   # set sample_rate to 1 if you wanna sampling 100% of trace data; set 0.5 if you wanna sampling 50% of trace data, and so forth
#   sample_rate: 1
#   # # namespace used to differenciate different harbor services
#   # namespace:
#   # # attributes is a key value dict contains user defined attributes used to initialize trace provider
#   # attributes:
#   #   application: harbor
#   # # jaeger should be 1.26 or newer.
#   # jaeger:
#   #   endpoint: http://hostname:14268/api/traces
#   #   username:
#   #   password:
#   #   agent_host: hostname
#   #   # export trace data by jaeger.thrift in compact mode
#   #   agent_port: 6831
#   # otel:
#   #   endpoint: hostname:4318
#   #   url_path: /v1/traces
#   #   compression: false
#   #   insecure: true
#   #   # timeout is in seconds
#   #   timeout: 10

# Enable purge _upload directories
upload_purging:
  enabled: true
  # remove files in _upload directories which exist for a period of time, default is one week.
  age: 168h
  # the interval of the purge operations
  interval: 24h
  dryrun: false

# Cache layer configurations
# If this feature enabled, harbor will cache the resource
# `project/project_metadata/repository/artifact/manifest` in the redis
# which can especially help to improve the performance of high concurrent
# manifest pulling.
# NOTICE
# If you are deploying Harbor in HA mode, make sure that all the harbor
# instances have the same behaviour, all with caching enabled or disabled,
# otherwise it can lead to potential data inconsistency.
cache:
  # not enabled by default
  enabled: false
  # keep cache for one day by default
  expire_hours: 24

# Harbor core configurations
# Uncomment to enable the following harbor core related configuration items.
# core:
#   # The provider for updating project quota(usage), there are 2 options, redis or db,
#   # by default is implemented by db but you can switch the updation via redis which
#   # can improve the performance of high concurrent pushing to the same project,
#   # and reduce the database connections spike and occupies.
#   # By redis will bring up some delay for quota usage updation for display, so only
#   # suggest switch provider to redis if you were ran into the db connections spike aroud
#   # the scenario of high concurrent pushing to same project, no improvment for other scenes.
#   quota_update_provider: redis # Or db
1.6 编写tasks文件
在main.yml入口引用相关的tasks部署任务文件。
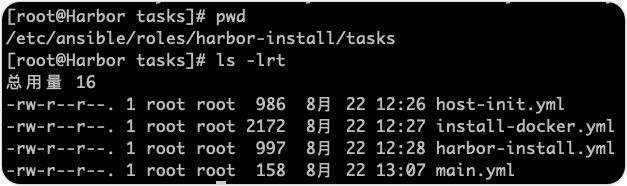
$ cat roles/harbor-install/tasks/main.yml
---
- include_tasks: host-init.yml
- include_tasks: install-docker.yml
- include_tasks: harbor-install.yml
1)编写主机初始化的tasks
$ cat roles/harbor-install/tasks/host-init.yml
---
#主机初始化配置

- name: "关闭SELinux(临时)"
  selinux:
    state: disabled

- name: "关闭SELinux(永久)"
  lineinfile:
    path: /etc/selinux/config
    regexp: '^SELINUX='
    line: 'SELINUX=disabled'
    create: yes

- name: "停止firewalld"
  service:
    name: firewalld
    state: stopped
    enabled: no
  ignore_errors: yes

- name: "停止iptables"
  service:
    name: iptables
    state: stopped
    enabled: no
  ignore_errors: yes

- name: "加载内核模块"
  shell:
    cmd: "modprobe br_netfilter"

- name: "设置内核参数(必须)"
  sysctl:
    name: "{{ item.key }}"
    value: "{{ item.value }}"
    sysctl_set: yes
    state: present
    reload: yes
  loop:
    - { key: 'net.ipv4.ip_forward', value: '1' }
    - { key: 'net.bridge.bridge-nf-call-iptables', value: '1' }
    - { key: 'net.bridge.bridge-nf-call-ip6tables', value: '1' }

- name: "创建安装目录"
  file:
    path: "{{ INSTALL_PATH }}"
    state: directory
- 2)编写安装docker的tasks
编写一个tasks任务,用于二进制安装containerd、docker和docker-compose服务。
$ cat roles/harbor-install/tasks/install-docker.yml
#二进制方式安装docker-ce、docker-compose
---
#当docker命令返回非零状态码时,即未安装时执行安装docker任务
- name: "检查docker是否安装"
  shell: docker --version
  register: docker_version
  ignore_errors: true

- name: "若未安装docker则安装(二进制)"
  when: docker_version.rc != 0
  block:
  - name: "分发docker-ce离线二进制安装包"
    unarchive:
      src: "docker-{{ DOCKER_VERSION }}.tgz"
      dest: "{{ INSTALL_PATH }}/"
      mode: 0755

  - name: "复制二进制文件到/usr/bin/下"
    copy:
      src: "{{ INSTALL_PATH }}/docker/{{ item }}"
      dest: "/usr/bin/"
      mode: '0755'
      remote_src: yes
    loop:
    - containerd
    - containerd-shim
    - containerd-shim-runc-v2
    - ctr
    - docker
    - dockerd
    - docker-init
    - docker-proxy
    - runc

  - name: "清理安装包"
    file:
      path: "{{ INSTALL_PATH }}/docker"
      state: absent

  - name: "创建docker用户组"
    group:
      name: docker
      state: present
      system: yes
      create_home: no
  #- name: "分发docker配置文件"
  #  copy:
  #    src: daemon.json
  #    dest: /etc/docker/
  #    mode: '0755'

  - name: "分发docker.socket文件(必需)"
    copy:
      dest: /usr/lib/systemd/system/docker.socket
      mode: '0644'
      content: |
        [Unit]
        Description=Docker Socket for the API
        [Socket]
        ListenStream=/var/run/docker.sock
        SocketMode=0660
        SocketUser=root
        SocketGroup=docker
        [Install]
        WantedBy=sockets.target

  - name: "分发containerd服务启动文件"
    copy:
      src: containerd.service
      dest: /usr/lib/systemd/system/containerd.service
      mode: '0644'

  - name: "分发docker服务启动文件"
    copy:
      src: docker.service
      dest: /usr/lib/systemd/system/docker.service
      mode: '0644'

  - name: "启动docker服务"
    service:
      name: docker
      state: started
      enabled: yes
      daemon_reload: yes

- name: "安装docker-compose(二进制)"
  copy:
    src: docker-compose-linux-x86_64
    dest: /usr/local/bin/docker-compose
    mode: '0755'
- 3)编写安装harbor的tasks文件
$ cat roles/harbor-install/tasks/harbor-install.yml
---
- name: "创建数据目录"
  file:
    path: "{{ DATA_PATH }}"
    state: directory

- name: "分发离线安装包"
  unarchive:
    src: "harbor-offline-installer-v{{ HARBOR_VERSION }}.tgz"
    dest: "{{ INSTALL_PATH }}"

- name: "分发配置文件"
  template:
    src: harbor.yml.j2
    dest: "{{ INSTALL_PATH }}/harbor/harbor.yml"

- name: "导入镜像 <docker load  -i xxx.tar.gz>"
  shell:
    cmd: "docker load  -i harbor.v{{ HARBOR_VERSION }}.tar.gz "
    chdir: "{{ INSTALL_PATH }}/harbor"

- name: "将配置文件注入到组件中 <./prepare>"
  shell:
    cmd: "./prepare"
    chdir: "{{ INSTALL_PATH }}/harbor"

- name: "安装并启动服务 <./install.sh --with-trivy>"
  shell:
    cmd: "./install.sh --with-trivy"
    chdir: "{{ INSTALL_PATH }}/harbor"

- name: "查看服务状态<docker-compose ps>"
  shell:
    cmd: docker-compose ps
    chdir: "{{ INSTALL_PATH }}/harbor"
  register: docker_compose_output

- debug:
     msg: "{{ docker_compose_output.stdout }}"
至此,部署harbor的ansible role编写就完成了,下面说明如何使用。
二、ansible部署Harbor
使用前面创建好的ansible role来部署Harbor镜像仓库服务。
2.1 创建ansible plabook
$ cat Playbooks/harbor-deploy.yml
---
- hosts: harbor       #指定部署Harbor的主机
  become: yes
  roles:
  - harbor-install    #调用安装harbor的ansible role
2.2 执行ansible plabook任务
$ ansible-playbook Playbooks/harbor-deploy.yml
[root@lidabai-console ansible]# ansible-playbook Plabooks/harbor-deploy.yml

PLAY [harbor] **********************************************************************************************

TASK [Gathering Facts] *************************************************************************************
ok: [harbor]

TASK [harbor-install : include_tasks] **********************************************************************
included: /etc/ansible/roles/harbor-install/tasks/host-init.yml for harbor

TASK [harbor-install : 关闭SELinux(临时)] ****************************************************************
ok: [harbor]

TASK [harbor-install : 关闭SELinux(永久)] ****************************************************************
ok: [harbor]

TASK [harbor-install : 停止firewalld] **********************************************************************
ok: [harbor]

TASK [harbor-install : 停止iptables] ***********************************************************************
fatal: [harbor]: FAILED! => {"changed": false, "msg": "Could not find the requested service iptables: host"}
...ignoring

TASK [harbor-install : 加载内核模块] ***********************************************************************
changed: [harbor]

TASK [harbor-install : 设置内核参数(必须)] ***************************************************************
ok: [harbor] => (item={'key': 'net.ipv4.ip_forward', 'value': '1'})
ok: [harbor] => (item={'key': 'net.bridge.bridge-nf-call-iptables', 'value': '1'})
ok: [harbor] => (item={'key': 'net.bridge.bridge-nf-call-ip6tables', 'value': '1'})

TASK [harbor-install : 创建安装目录] ***********************************************************************
ok: [harbor]

TASK [harbor-install : include_tasks] **********************************************************************
included: /etc/ansible/roles/harbor-install/tasks/install-docker.yml for harbor

TASK [harbor-install : 检查docker是否安装] *****************************************************************
changed: [harbor]

TASK [harbor-install : 分发docker-ce离线二进制安装包] ******************************************************
skipping: [harbor]

TASK [harbor-install : 复制二进制文件到/usr/bin/下] ********************************************************
skipping: [harbor] => (item=containerd)
skipping: [harbor] => (item=containerd-shim)
skipping: [harbor] => (item=containerd-shim-runc-v2)
skipping: [harbor] => (item=ctr)
skipping: [harbor] => (item=docker)
skipping: [harbor] => (item=dockerd)
skipping: [harbor] => (item=docker-init)
skipping: [harbor] => (item=docker-proxy)
skipping: [harbor] => (item=runc)
skipping: [harbor]

TASK [harbor-install : 清理安装包] *************************************************************************
skipping: [harbor]

TASK [harbor-install : 分发docker配置文件] *****************************************************************
skipping: [harbor]

TASK [harbor-install : 分发docker.socket文件(必需)] ******************************************************
skipping: [harbor]

TASK [harbor-install : 分发containerd服务启动文件] *********************************************************
skipping: [harbor]

TASK [harbor-install : 分发docker服务启动文件] *************************************************************
skipping: [harbor]

TASK [harbor-install : 创建docker用户组] *******************************************************************
skipping: [harbor]

TASK [harbor-install : 启动docker服务] *********************************************************************
skipping: [harbor]

TASK [harbor-install : 安装docker-compose(二进制)] *******************************************************
ok: [harbor]

TASK [harbor-install : include_tasks] **********************************************************************
included: /etc/ansible/roles/harbor-install/tasks/harbor-install.yml for harbor

TASK [harbor-install : 创建数据目录] ***********************************************************************
ok: [harbor]

TASK [harbor-install : 分发离线安装包] *********************************************************************
ok: [harbor]

TASK [harbor-install : 分发配置文件] ***********************************************************************
ok: [harbor]

TASK [harbor-install : 导入镜像 <docker load  -i xxx.tar.gz>] **********************************************

changed: [harbor]

TASK [harbor-install : 将配置文件注入到组件中 <./prepare>] *******************************************************************************************************************
changed: [harbor]

TASK [harbor-install : 安装并启动服务 <./install.sh --with-trivy>] *******************************************************************************************************
changed: [harbor]

TASK [harbor-install : 查看服务状态<docker-compose ps>] *****************************************************************************************************************
changed: [harbor]

TASK [harbor-install : debug] *************************************************************************************************************************************
ok: [harbor] => {
    "msg": "NAME                COMMAND                  SERVICE             STATUS               PORTS\nharbor-core         \"/harbor/entrypoint.…\"   core                running (starting)   \nharbor-db           \"/docker-entrypoint.…\"   postgresql          running (starting)   \nharbor-jobservice   \"/harbor/entrypoint.…\"   jobservice          restarting           \nharbor-log          \"/bin/sh -c /usr/loc…\"   log                 running (starting)   127.0.0.1:1514->10514/tcp\nharbor-portal       \"nginx -g 'daemon of…\"   portal              running (starting)   \nnginx               \"nginx -g 'daemon of…\"   proxy               running (starting)   0.0.0.0:8021->8080/tcp, :::8021->8080/tcp\nredis               \"redis-server /etc/r…\"   redis               running (starting)   \nregistry            \"/home/harbor/entryp…\"   registry            running (starting)   \nregistryctl         \"/home/harbor/start.…\"   registryctl         running (starting)   \ntrivy-adapter       \"/home/scanner/entry…\"   trivy-adapter       running (starting)   "
}

PLAY RECAP ********************************************************************************************************************************************************
harbor              : ok=29   changed=16   unreachable=0    failed=0    skipped=0    rescued=0    ignored=3
部署完成!


